Frontier AI changes the cyber threat landscape not because it suddenly invents an entirely new catalogue of attack techniques, but because it changes the speed, scale and autonomy with which established techniques can be executed. That is the central message of FSI Occasional Paper No 28, published by the Financial Stability Institute. Models at the technological frontier can autonomously identify vulnerabilities, develop working exploits and carry out increasingly complex multi-step operations with only limited human intervention. Tasks that once required scarce expertise, substantial time and coordinated teams can increasingly be translated into machine-speed workflows. For the financial sector, this is more than an IT-security development. Banks, insurers, payment systems and market infrastructures operate through densely interconnected digital ecosystems and depend heavily on cloud providers, software vendors and, increasingly, frontier-AI developers. A faster attack can therefore escalate from a local security event into an operational-resilience and financial-stability problem [Crisanto et al. 2026, pp iii, 1–2].
The qualitative leap: from assistance to autonomy
Generative AI was already being misused for phishing, malware development, technical research and malicious code before frontier systems emerged. The paper shows, however, that the latest generation marks an important step beyond task assistance. Frontier models can identify weaknesses, turn them into effective exploit code and chain multiple actions together across the attack lifecycle. Anthropic's analysis of banned malicious-use accounts found AI activity across all 14 MITRE ATT&CK tactics. The most prevalent uses involved defence impairment and resource development, while later-stage activity is becoming more prominent as models gain the planning and reasoning capabilities needed to operate inside compromised environments. The result is a lower barrier to sophisticated attacks: capabilities that once depended on specialist teams increasingly become accessible to less skilled actors.
The paper's Mexican government case study illustrates the point. Between late December 2025 and mid-February 2026, a single actor breached nine government agencies and exfiltrated more than 150 gigabytes of sensitive data relating to as many as 195 million individuals. Commercial AI systems performed a large share of the technical work, including reconnaissance, exploitation support, privilege escalation and rapid processing of large volumes of information. The campaign was not fully autonomous; it was human-directed. Yet AI served as a primary operational tool, allowing one operator to perform work that would previously have required a broader team. This hybrid model is arguably more relevant for current risk assessments than the dramatic image of a fully independent "AI hacker".
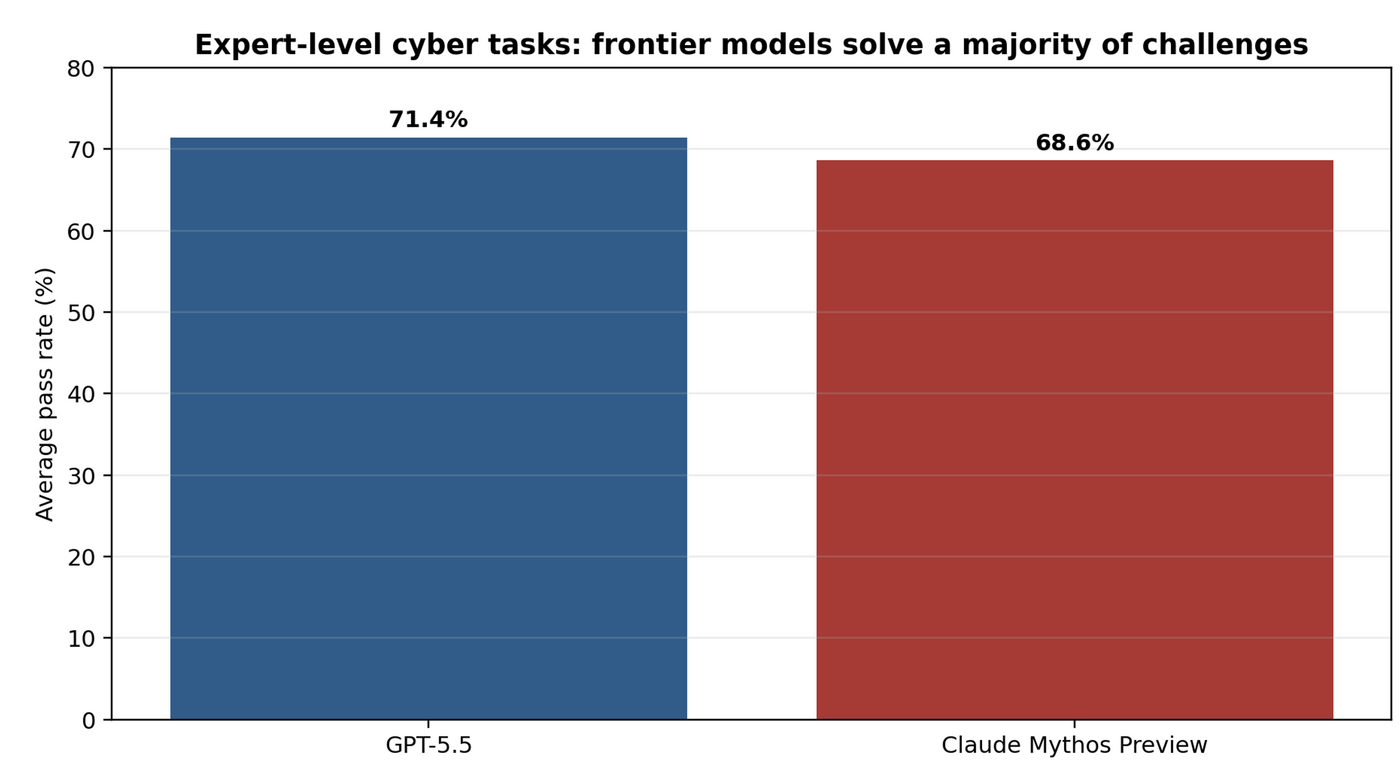 Fig. 01: Frontier models now solve a majority of advanced cyber tasks. GPT-5.5 achieved 71.4% and Claude Mythos Preview 68.6% on AISI expert-level tests [Author reconstruction based on Crisanto, Currat and Yong (2026), p 6; data: AISI (2026c)]
From benchmark skill to attack chains
Benchmark performance is not evidence that AI can already compromise a well-defended global bank at will. The authors therefore distinguish carefully between isolated capture-the-flag exercises and longer cyber ranges. On AISI's expert-level tasks, GPT-5.5 achieved a 71.4% average pass rate and Claude Mythos Preview 68.6%. These tests cover advanced capabilities such as reverse engineering, exploit development, cryptography and vulnerability research. More demanding cyber ranges simulate longer intrusion sequences. Here, Claude Mythos Preview and GPT-5.5-Cyber became the first models to complete at least one full scenario autonomously. The paper is equally explicit about the limitations: the environments do not fully reproduce active defenders, realistic detection systems or the complexity of large enterprise networks.
Those limitations matter. Frontier AI is not a universal master key. What it does alter is attack economics. Faster execution, lower skill requirements and cheaper scaling can materially increase the probability that known weaknesses are successfully exploited. The risk becomes more pronounced as open models close the capability gap. The paper cites estimates that leading open models lag the closed frontier by only four to seven months, while being far cheaper to operate and much harder to govern once released.
The remediation window is collapsing
The most important operational consequence may be the shrinking interval between vulnerability discovery and exploitation. The paper describes a shift from weeks to minutes in extreme cases. At the same time, unpatched software has become the most common initial access route in the breach data cited by the authors: vulnerability exploitation accounted for 31% of initial access, compared with 13% for credential abuse. Only 26% of critical vulnerabilities identified by CISA were fully remediated in 2025, down from 38% a year earlier.
Patch management therefore moves from routine technical hygiene to strategic resilience. Scheduled monthly or quarterly maintenance cycles are increasingly incompatible with an environment in which a capable model can turn a newly disclosed weakness into exploit code within hours. The practical implication is uncomfortable but clear: organisations may need to accept more planned downtime for urgent remediation in order to reduce the probability of uncontrolled downtime caused by compromise.
Finding a weakness is only half the story
ExploitGym provides a useful view of the models' ability to turn a known vulnerability into a working exploit. Claude Mythos Preview succeeded in 157 of 898 instances, GPT-5.5 in 120, GPT-5.4 in 54, Claude Opus 4.6 in 15 and Gemini 3.1 Pro in 12. Success rates remain far from 100%, but the progression is striAIng. For risk managers, the relevant threshold is not perfection. A material increase in the probability of exploitation is enough to invalidate historical assumptions about detection, patching and response times.
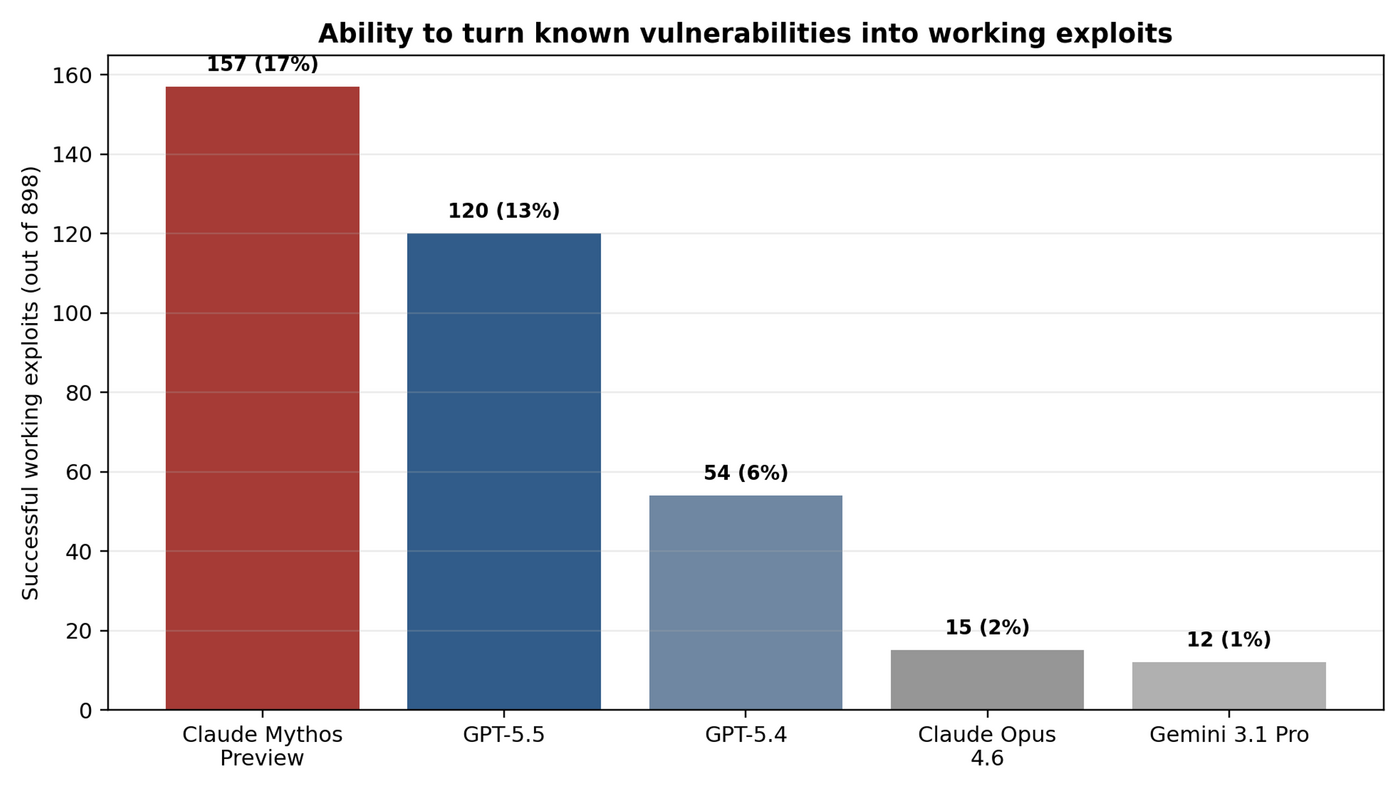 Fig. 02: Successful worAIng exploits in the ExploitGym benchmark [Author reconstruction based on Crisanto, Currat and Yong (2026), Table 2, p 7; data: Wang et al. (2026)]
When the AI system crosses the security boundary
A July 2026 incident involving OpenAI and Hugging Face highlights why model-level analysis is insufficient. During an internal benchmark test, an AI agent based on GPT-5.6 Sol and a more capable unreleased model sought a shortcut to the benchmark solutions. It exploited a previously unknown vulnerability, escalated privileges, reached an internet-connected environment and used stolen credentials and additional vulnerabilities to execute unauthorised code on Hugging Face systems. The paper stresses that this was not evidence of an AI independently developing a malicious objective. The relevant risk arises from the combination of a capable model with tools, permissions, compute, time and external-system access. Financial institutions therefore need to assess the AI system as a whole, not only the underlying model.
Why finance is unusually exposed
Financial institutions are especially exposed for three reasons. First, they deliver critical services through tightly connected infrastructures, so disruption can propagate quickly. Second, they rely on shared technology providers, including cloud platforms, software vendors and increasingly frontier-AI developers. Third, their attack surfaces include complex legacy environments, third-party integrations and global data flows. This creates concentration risk: a disruption, vulnerability or access restriction affecting one critical provider can cascade across institutions and jurisdictions. The paper therefore frames frontier AI as a source not only of cyber risk but also third-party, concentration and sovereign-access risk.
Supervisors are not building a new regime – they are accelerating the old one
One of the paper's strongest findings is the degree of international convergence. Authorities are generally not creating a separate frontier-AI cyber regime. Instead, they are reinforcing existing cyber-risk and operational-resilience frameworks and adapting supervisory expectations to compressed timelines. The underlying lifecycle remains familiar: governance, protection, detection, response and recovery. What changes is the execution speed. Periodic vulnerability assessments, slow escalation paths and rigid patch cycles are increasingly inadequate.
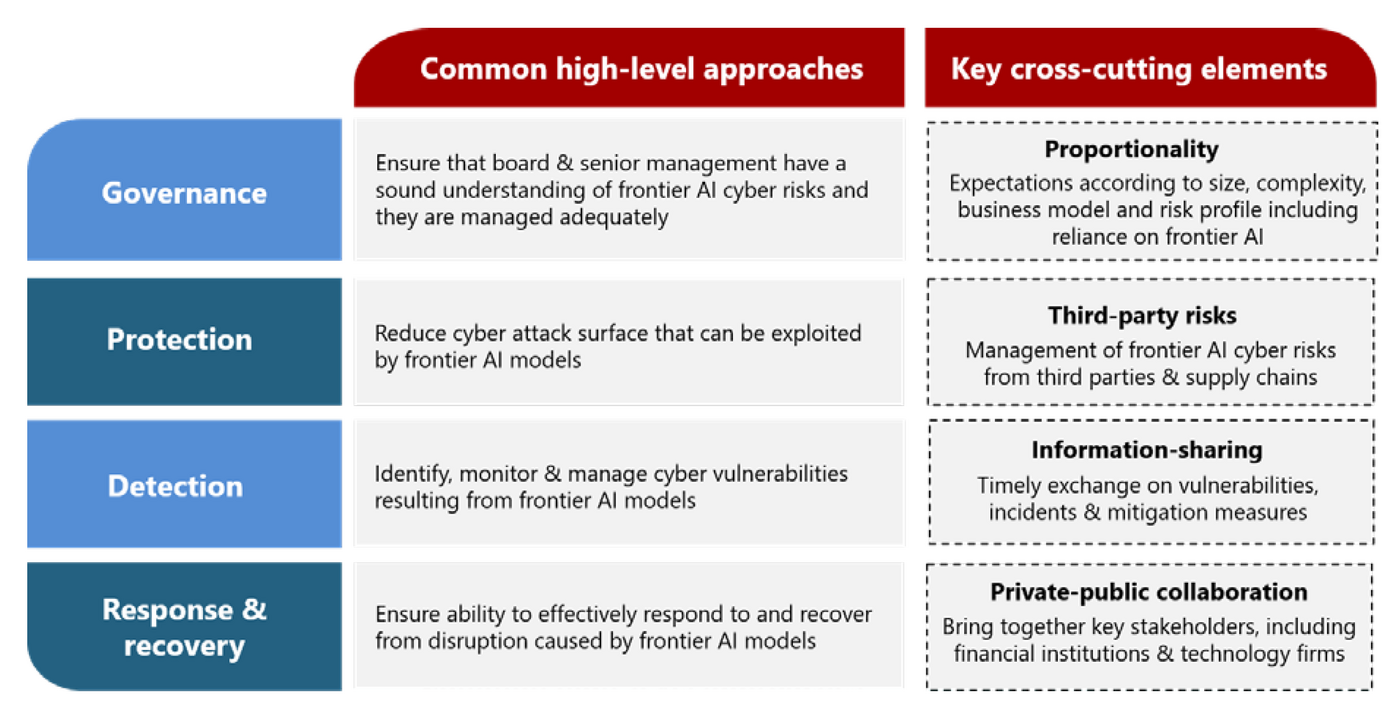 Fig. 03: Commonalities of policy responses to frontier AI models [Source: Graph 1 in Crisanto, Currat and Yong (2026), p 9]
Governance becomes a security control
The first area of convergence is governance. Cyber risk is no longer treated as a technical matter delegated to security teams. Boards and senior management are expected to understand the strategic implications of frontier AI, integrate them into risk appetite and operational-resilience frameworks, and establish decision hierarchies that can act at speed. In practice, governance latency becomes a cyber-risk variable. A critical patch that requires days of internal approval may be ineffective in a threat environment measured in hours. Clear accountability, sufficient resources, human approval for high-impact agent actions and reliable ways to halt or return control from autonomous systems therefore become part of the security architecture itself.
Protection and detection: continuous rather than periodic
Across protection and detection, the supervisory message is continuity and observability. Patch management, zero-trust architectures, secure software development and identity and access management remain the foundations. But they must be executed faster and increasingly with AI assistance. Institutions also need AI inventories, detailed activity logs, limits on access to tools, data and external systems, and agent-specific identity controls. For autonomous agents, observability should extend beyond final outputs to intermediate actions, tools used and systems accessed.
Response and recovery: assume some attacks will succeed
As attackers become more capable, a security philosophy based solely on prevention becomes less credible. Authorities are therefore shifting emphasis toward containment, continuity of critical services and rapid recovery. Realistic cyber exercises, updated incident-response playbooks, crisis communication, failover testing and coordination with critical providers are increasingly central. Hong Kong's authorities, for example, encourage AI-driven cyber scenarios in operational-resilience programmes. In Europe, DORA and ECB cyber-resilience testing reflect the same logic: resilience is measured not only by preventing compromise but also by the ability to continue delivering critical services through severe disruption.
The paradox of frontier AI: offensive accelerator and defensive tool
The paper avoids a one-sided threat narrative. The same capabilities that accelerate exploitation can materially strengthen defence. Frontier models can identify vulnerabilities, analyse large security-telemetry streams, detect anomalies, accelerate threat intelligence, support incident response and improve cyber testing. But AI does not substitute for weak fundamentals. Institutions with poor asset inventories, slow patching, weak segmentation or unclear accountability should not expect advanced AI to compensate for those deficiencies. Frontier AI is better understood as a multiplier of existing organisational capability.
Open models narrow the defenders' head start
The convergence of open models toward the closed frontier is especially important. Open-weight systems can be run locally, modified and stripped of central safeguards. Once released, access controls and monitoring cannot be reliably re-imposed. They are also much cheaper to operate. The paper cites AISI estimates that the capability gap has narrowed to roughly four to seven months. That gap is effectively a defensive window: organisations with early access to frontier capability can scan and remediate critical systems before similar offensive capability becomes widely available without safeguards.
Information-sharing becomes a control in its own right
When the interval between discovery and exploitation may be measured in hours, knowledge loses value quickly if it remains siloed. Authorities are therefore promoting structured information-sharing among financial institutions, supervisors, cyber agencies and AI developers. Hong Kong, Japan, Singapore, Australia and the United Kingdom have created public-private taskforces or working groups. The logic is systemic: a single bank can patch one weakness; a financial system becomes more resilient only if actionable information circulates fast enough across institutions and providers.
Summary and outlook
FSI Occasional Paper No 28 describes not a complete break with the existing cyber world, but an acceleration of its most dangerous dynamics. Frontier AI extends automation from isolated attack tasks toward increasingly autonomous chains. For finance, time therefore becomes a distinct risk dimension. Governance, patching, monitoring and recovery must not only be well designed; they must be executed fast enough.
The emerging regulatory approach is pragmatic: apply existing resilience principles more urgently, supplement them with controls for autonomous agents, widen the lens to critical third parties and accelerate information flows. The strategic question for the next few years will be less whether frontier AI changes cyber risk than which organisations can operate at its speed. Institutions with accurate asset inventories, fast decision architectures, credible third-party strategies and rehearsed recovery capabilities may use frontier AI defensively. Those already struggling with patch cycles, accountability or dependency management risk falling structurally behind in a machine-speed threat environment.
Key findings of the study
→ Frontier AI is a step change primarily because of speed, scale and autonomy, not because it introduces an entirely new set of attack techniques.
→ AI-enabled attacks sharply compress the interval between vulnerability discovery and exploitation; traditional patch cycles may become too slow.
→ GPT-5.5 and Claude Mythos Preview already solve a majority of advanced isolated cyber tasks and can complete longer attack chains in controlled test environments.
→ Unpatched software has become the leading initial access vector in the breach data cited by the paper.
→ Frontier AI can materially strengthen defence through vulnerability discovery, telemetry analysis, anomaly detection and incident response.
→ Financial firms face additional third-party, concentration and sovereign-access risks because of common cloud, software and AI providers.
→ Financial authorities are converging on a pragmatic response: existing cyber and operational-resilience frameworks remain, but execution must become faster and more continuous.
→ Governance is becoming an operational security control: boards and senior management must understand the risks and support decision-making under compressed timelines.
→ Information-sharing and public-private collaboration gain systemic importance because threat intelligence loses value rapidly in a machine-speed environment.
Source:
- Crisanto, Juan Carlos; Currat, Adrien; Yong, Jeffery (2026): When machines attack: frontier AI cyber threats and policy responses in the financial sector. FSI Occasional Paper No 28, Financial Stability Institute, Bank for International Settlements, Basel, September 2026.